
HOW to Utilize LAPS from Intune But Not Get Rid of SCCM
Question
Hi All,
Sorry for asking a dumb question. I would like to ask about best pratice to manage Windows devices. I do have On-prem AD and also SCCM. I want to utilize LAPS from Intune but not get rid of SCCM. I want to keep SCCM as I do receive Microsoft monthly updates, patching and software deployments. I have received an advise from MS Support that I should follow Co-MGMT but I’m not sure if it’s correct since that guys said he’s not sure about the situation too. https://learn.microsoft.com/…/deployment-guide…
I’m open mind for listening. Please advise me guys. TIA!
Posted by Caenapo Sanada in HTMD FB Groups

Answers ( 2 )
Replied by Caenapo Sanada
Sean Bravener Thank you for your comment. I do consider about migration completely to Cloud but maybe not now. Can I ask what is mag? Also, I do have pressing need for On-prem. Could I understand your statement that my goal is possible with Co-MGMT? Here’s my attempt with Co-MGMT, can you help me to check if I enrolled device correctly? Thank you Sean.
Replied by Caenapo Sanada
Fred van Workum Thank you for your suggestion. Can I ask you what is the difference between the Windows GPO enrollment and Co-MGMT? Because I was planning to do Windows enrollment with GPO but MSFT support said I have SCCM and I should go with Co-Mgmt. Below is screenshot of device in Intune and ENTRA portal. Could you please review to see if I enrolled correctly? Thank you Fred.
Replied by Sushant Vashist
We are using the same solution. It will work seamlessly. Go with what MS has suggested.
Replied by Caenapo Sanada
Thank you for your confirmation. I will try.
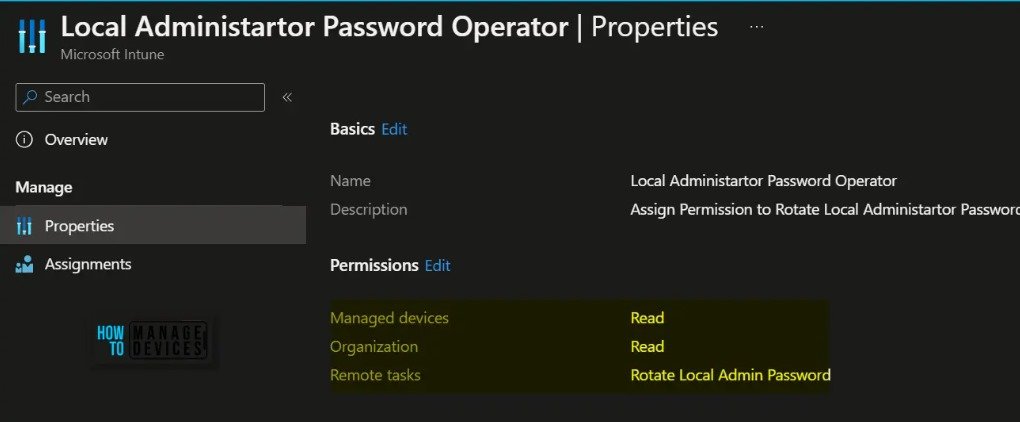
For More Details Windows LAPS Role Based Access Controls using Intune
https://www.anoopcnair.com/windows-laps-role-based-access-controls-intune/
Replied by Mike Leach
What Fred said! Co-Management! Intune does some things better than SCCM.
Replied by Fred van Workum
Co-management and in co-management, move Endpoint protection to Intune, but if you do your management in AD, I would expect that you also still use GPO’s, why not configure laps also with a GPO?, in the GPO you can still set to backup the admin password to ENTRA.
Replied by Sean Bravener
endpoint protection or policy would work in intune or laps gpo using on prem. If co-mgmt you also have to set up entra and mag since mag is required and best practice for entra now.
If you don’t have a pressing need for on prem you should look into migrating to Intune anyways as MS is trying to move that direction anyways.