
Running Executables Securely with Proactive Remediation via Intune
Question
Hi All,
I’m trying to use proactive remediation to run an executable. When I run the script manually, it downloads the executable from a URL to C:directory and then executes it. However, when I run the remediation script via Intune, it fails. I believe this is because it requires admin privileges. Is there a way I can securely run this without specifying admin account credentials within the script?
Posted by Anonymous member in HTMD FB Group

Answer ( 1 )
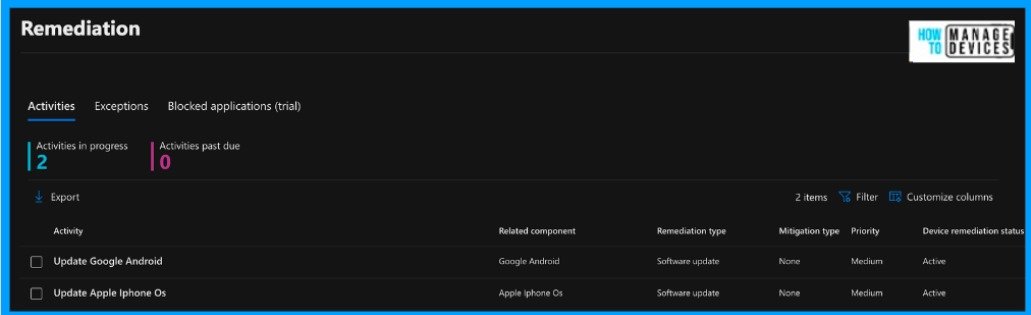
Fore More Details Best Way to Remediate Vulnerabilities with Microsoft Defender for Endpoint using Intune
https://www.anoopcnair.com/intune-remediate-vulnerabilities-ms-defender/
Replied by Nicky De Westelinck
Why don’t you put the exe in a Win32 app and Deploy it?
Replied by Anonymous member
Nicky De Westelinck I would like to leverage proactive remediation so that any devices lacking the app automatically receive it through the remediation process. The executable is for the Windows 22H2 update. For some reason, certain devices fail to update, so I’ve resorted to this method to automate it.
Replied by Simon Hardy
You could achieve the same thing with Requirements and Detection Rules for a Win32 App based deployment
Replied by Anonymous member
Simon Hardy Thanks I think that’ll work better. I’ll test it and feedback here